The platform
From found to renewed. All the way to served.
One place to see your certificates, decide how they change, and check the result on the systems people depend on.
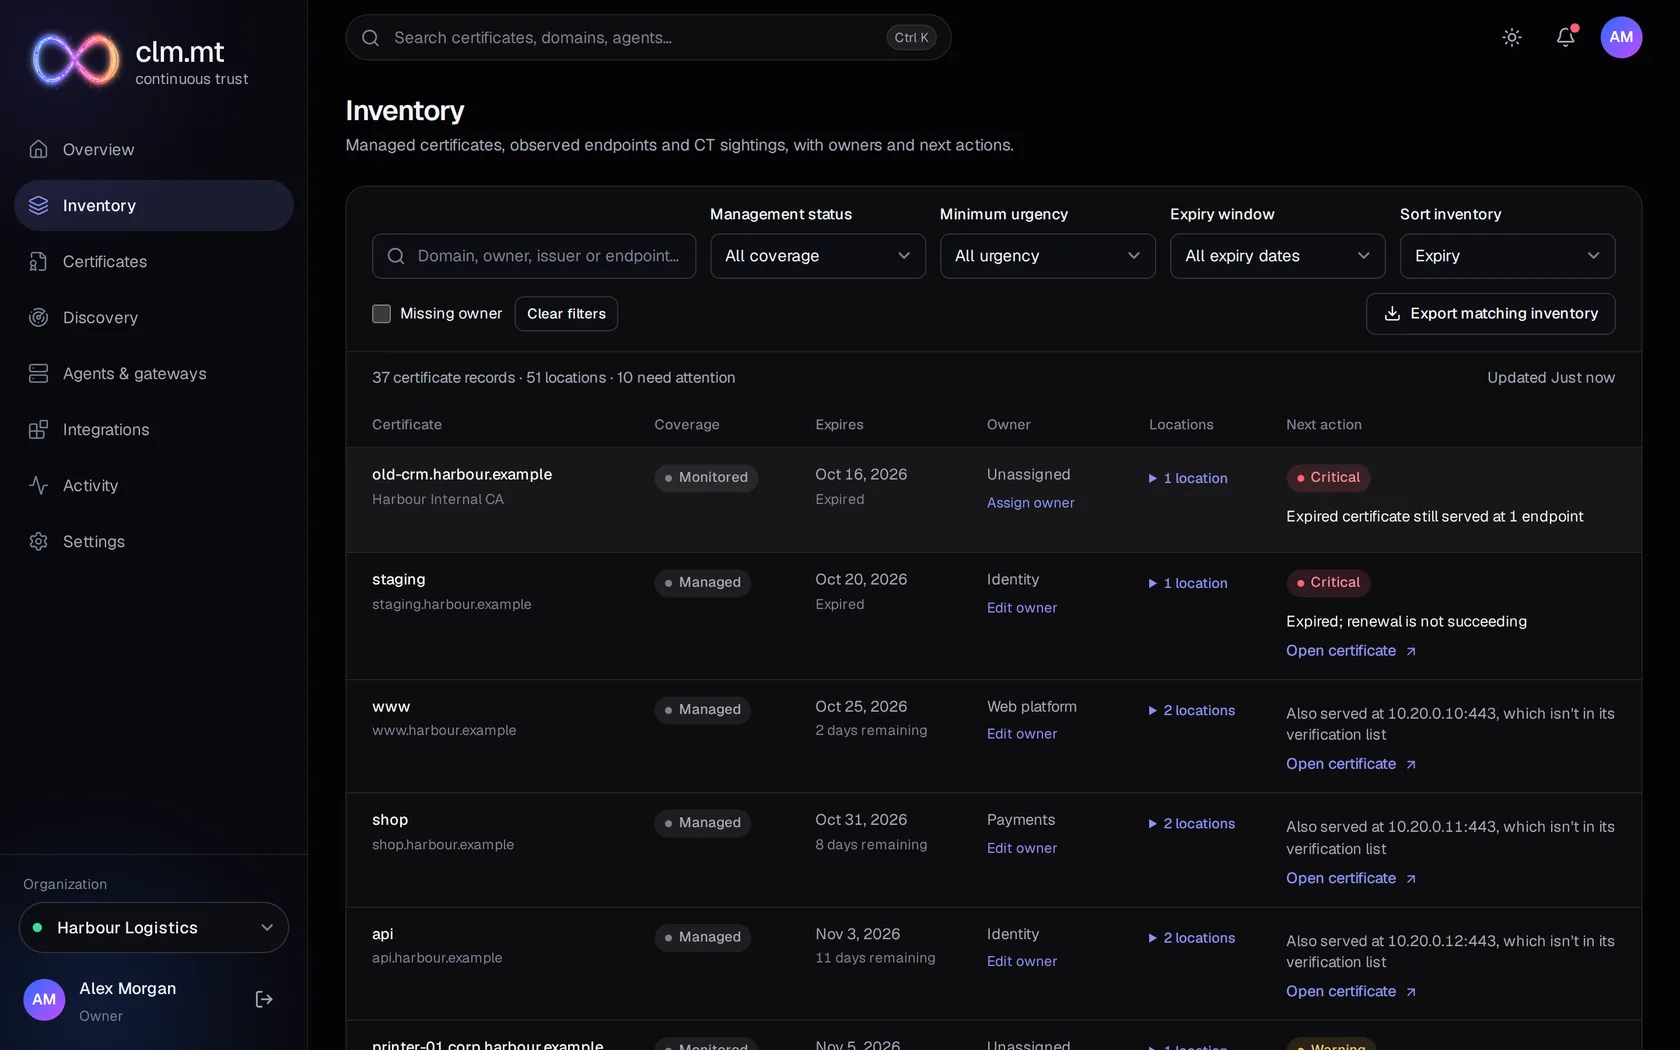
Real portal · fictional estate
A complete loop
Each step has a next step.
01Discover
Build the inventory.
Bring managed records, network observations and Certificate Transparency sightings into one view. Keep ownership and each serving location, even when several records share a certificate.
02Issue & renew
Use the CA you choose.
ACME with DNS-01, EAB for eligible accounts, renewal windows and pending-order recovery. Ordered failover respects your minimum validation level. A routine check never forces a new paid order.
03Deploy
Make the change deliberately.
Choose an agent or hosted runner, deployment targets, approval rules and maintenance windows. Failed rollouts attempt recovery using each connector’s supported rollback path; incomplete recovery needs operator attention.
04Verify
Check what is actually served.
Configure endpoint addresses and TLS server names. The runner checks the served certificate against the expected fingerprint after deployment. An installed file alone is not proof that the right certificate is live.
05 · Where the work runs
Central oversight. Local reach.
The central service holds policy, public certificate history, inventory and status. Installed agents connect outbound over HTTPS and reach private networks and local applications. Customers do not need to host the control plane.
Control plane
Embedded portal, API, scheduler and SQLite data directory. One active server process per installation; no active-active replicas.
Agents & gateways
Linux systemd and Windows Server 2022 installations with persistent identity, queued reports and signed worker updates. A gateway is the same agent reaching network targets.
Hosted runner
Runs eligible API-based work from the server. Its private keys are sealed on the control plane; hosted mode blocks private networks and ambient cloud credentials.
Daily operation
See the work that needs you.
- Attention queues and expiry buckets open the matching inventory view.
- Owners, locations and filtered CSV exports make handovers practical.
- Durable notifications and agent report replay preserve outcomes across outages.
Controlled changes
Policy follows the certificate.
- Role-based access, organisation boundaries and scoped API tokens.
- Distinct approvers, separation of duties and maintenance windows.
- Lifecycle history and a tamper-evident audit chain; external immutable anchoring is not built.
Start within the tested boundary
Preparing the service, with explicit limits.
The recorded single-organisation pilot covers 400 certificates, 40 agents and roughly 900 discovered endpoints. This is not a shared SaaS capacity guarantee. Connector validation varies, and commercial CA accounts need entitlement checks and staging acceptance. Multi-tenant scale and isolation review remains queued.
Check integration validation levels →See the loop in the product.
Explore the real Overview, Inventory and Discovery screens before planning your first deployment.